If everyone is responsible, no one really is. Fix this today.
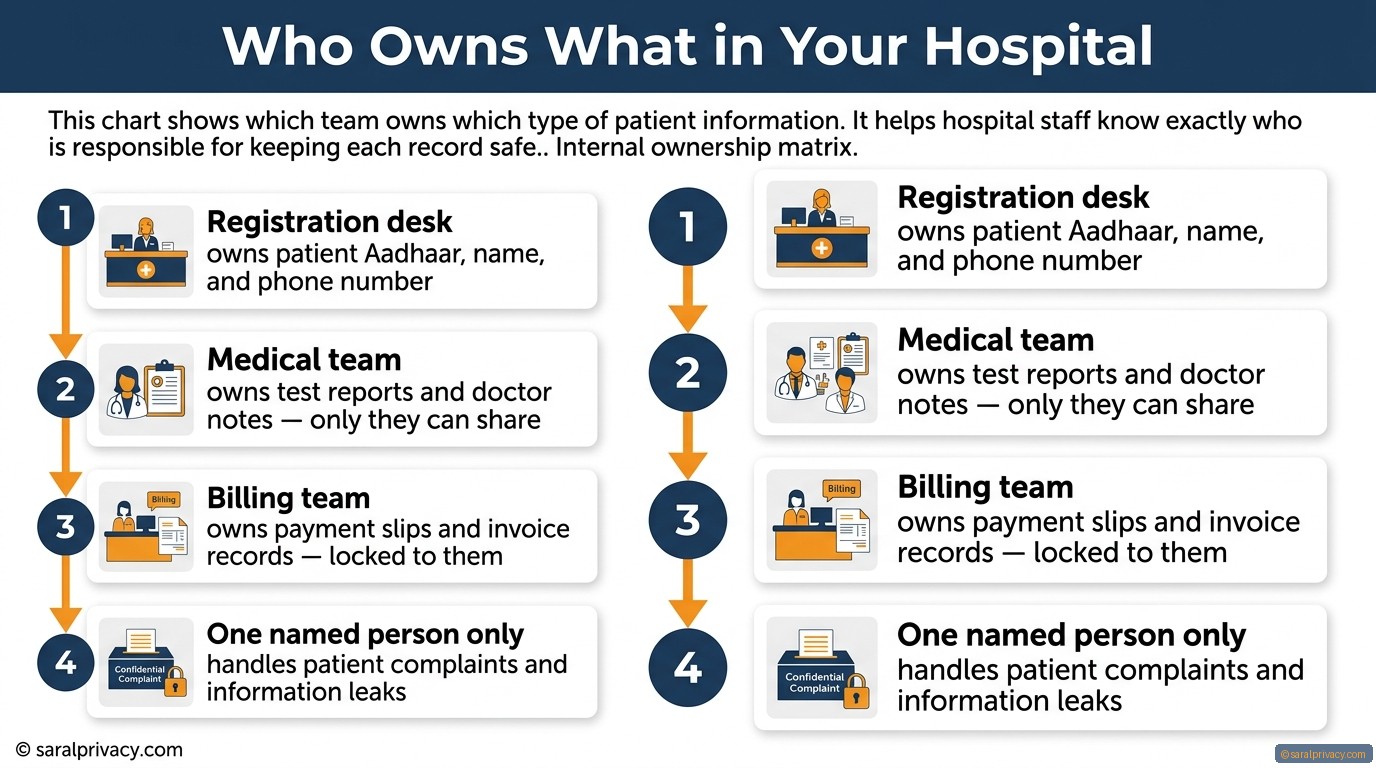
A patient shares their Aadhaar, phone number, and health reports at your hospital. Later, that information leaks. The police ask: who was in charge? Your team says 'everyone'. That answer will get your hospital in serious trouble. Under the new DPDPA law, hospitals must clearly decide who owns which information. No clear owner means no protection — and big fines.
Think of your hospital like a shop with many counters. The front desk collects patient names and Aadhaar. The lab holds test reports. The billing counter has payment slips. The admin team talks to vendors. Each counter must have one named person responsible. That person decides who can see the information. If a vendor asks for patient data, only one person can say yes or no. If a patient complains on WhatsApp, one person must reply and fix it. Without this split, your hospital breaks the law.
Write down one name for each type of patient information your hospital holds.
Tell your billing, registration, and lab teams what information only they can share.
Check if your business is ready. Takes 3 minutes. Visit saralprivacy.com/assessment
“A hospital cannot protect data with a job title called everyone.”
Free — takes 3 minutes
Answer a few simple questions. Get your free Readiness Score — sent to your email or WhatsApp.
Check My Readiness →Take our free 3–5 minute industry assessment to find out your compliance risk level.
Take Free Assessment →Free Download
The Complete DPDPA Compliance Guide
Plain English. Everything your business needs to understand the DPDP Rules 2025 — written for founders, not lawyers. Now in 7 Indian languages.
Download the Guide →5 Ready-to-Use Templates
Start complying — not just reading
Privacy Notice, Consent Language, Data Inventory, DSR SOP, Vendor Register. Delivered free to your email.
2-min reads, plain English, every morning. Free forever.
