Small NGOs use many tools — and each one can cause a big problem.
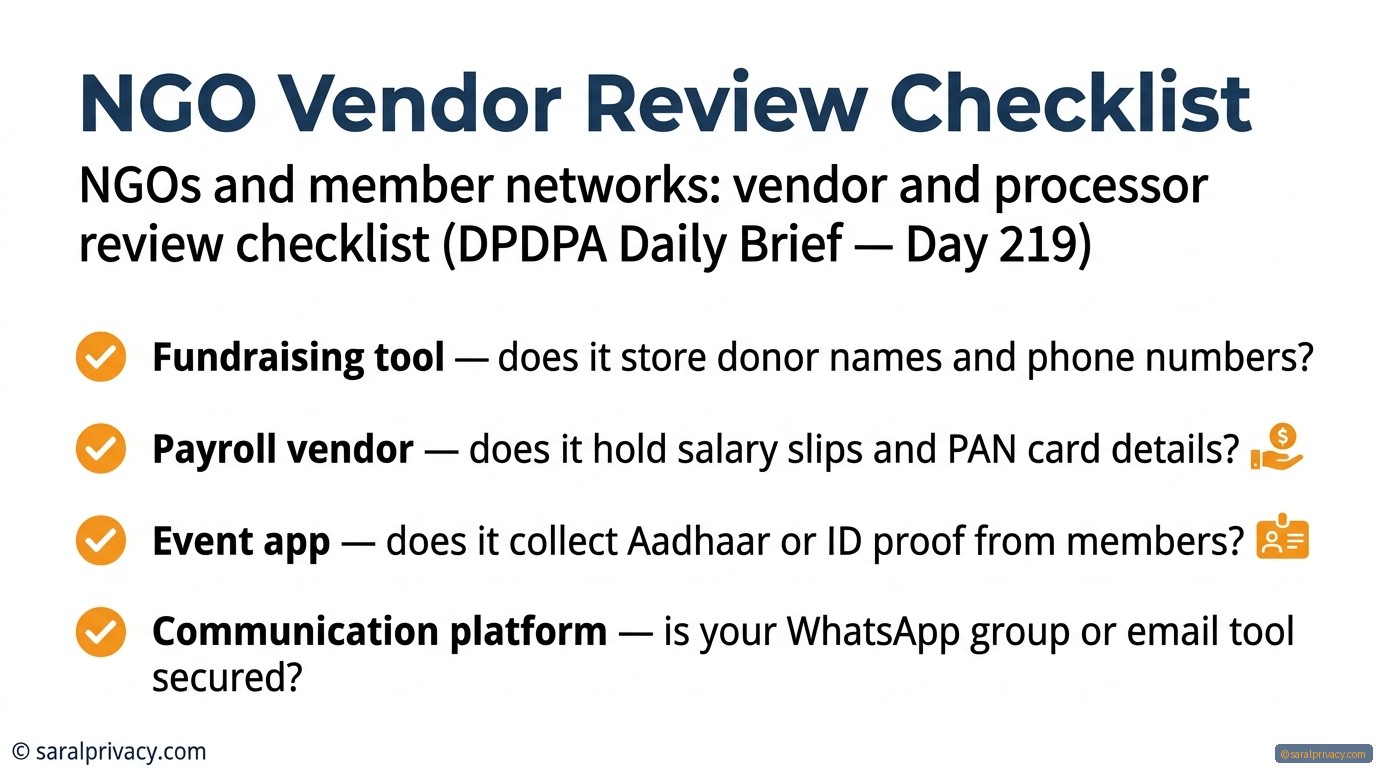
Your NGO collects names, phone numbers, and Aadhaar details of members and donors. You use apps for events, payroll, and WhatsApp groups for communication. But do you know who else can see that data? Under the DPDP Act, if a vendor misuses your members' information, YOUR NGO gets the fine — not the vendor. That fine can go up to ₹250 crore.
Think about all the tools your NGO uses. Your event registration app holds member phone numbers. Your payroll vendor holds salary slips and PAN card details. Your WhatsApp group has donor names. Your CRM has donor giving history. Each of these is a risk. You must check every vendor once. Ask: Do they have a signed agreement? Do they delete data when asked? Can they report a breach in 72 hours? Small teams need sharper vendor discipline, not less of it.
List every app and tool your NGO uses that holds people's information.
Check if each vendor has a signed data agreement — not just an NDA.
Check if your business is ready. Takes 3 minutes. Visit saralprivacy.com/assessment
“Small teams need sharper vendor discipline, not less of it.”
Free — takes 3 minutes
Answer a few simple questions. Get your free Readiness Score — sent to your email or WhatsApp.
Check My Readiness →Take our free 3–5 minute industry assessment to find out your compliance risk level.
Take Free Assessment →Free Download
The Complete DPDPA Compliance Guide
Plain English. Everything your business needs to understand the DPDP Rules 2025 — written for founders, not lawyers. Now in 7 Indian languages.
Download the Guide →5 Ready-to-Use Templates
Start complying — not just reading
Privacy Notice, Consent Language, Data Inventory, DSR SOP, Vendor Register. Delivered free to your email.
2-min reads, plain English, every morning. Free forever.
