Every vendor you share patient info with is your responsibility under the law.
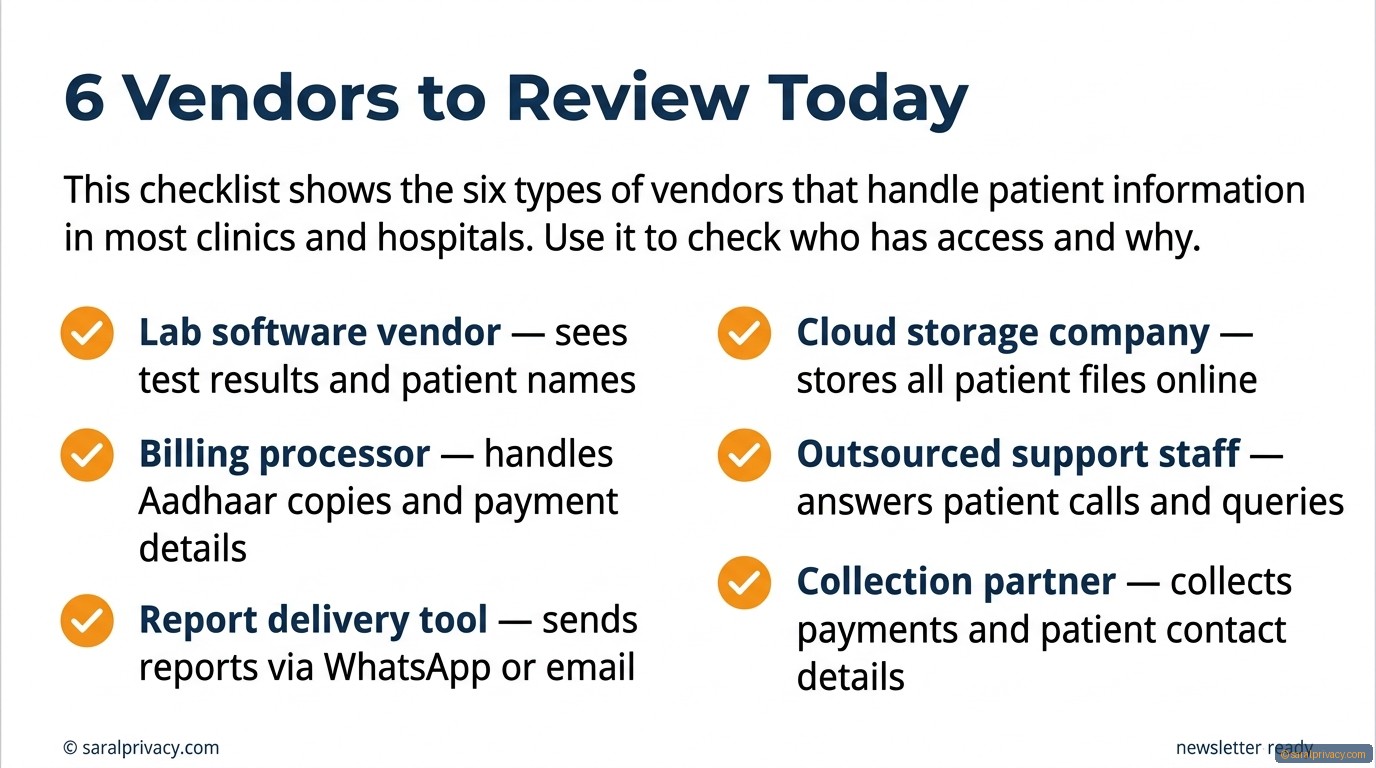
Your hospital or clinic shares patient information with many outside companies. Lab software, billing tools, report delivery apps — all of them touch patient data. If even one of them misuses it, the law holds YOU responsible. Most small hospitals never check their vendors. That is a big mistake. Today we show you a simple checklist to fix this before it becomes a problem.
Say your clinic uses a lab software company. They store patient names, mobile numbers, and blood reports. Now imagine they share that data with another company without telling you. The law says you are responsible. Same with your billing processor who handles Aadhaar copies. Or your WhatsApp-based report delivery tool. You must ask each vendor one simple question: why do you need this patient information? If they cannot answer clearly, stop sharing data with them.
List every vendor who receives patient names, numbers, or reports.
Ask each vendor in writing why they need patient information.
Check if your business is ready. Takes 3 minutes. Visit saralprivacy.com/assessment
“Every healthcare vendor touching patient data should pass one serious question: why do they need it.”
Free — takes 3 minutes
Answer a few simple questions. Get your free Readiness Score — sent to your email or WhatsApp.
Check My Readiness →Take our free 3–5 minute industry assessment to find out your compliance risk level.
Take Free Assessment →मुफ़्त डाउनलोड
संपूर्ण DPDPA अनुपालन गाइड
आसान भाषा में। DPDP Rules 2025 समझने के लिए आपके व्यवसाय को जो कुछ चाहिए — फ़ाउंडर्स के लिए लिखा गया, वकीलों के लिए नहीं। अब 7 भारतीय भाषाओं में।
गाइड डाउनलोड करें →5 तैयार टेम्पलेट
सिर्फ़ पढ़िए नहीं — अनुपालन शुरू कीजिए
प्राइवेसी नोटिस, सहमति की भाषा, डेटा इन्वेंटरी, DSR SOP, वेंडर रजिस्टर। आपके ईमेल पर, मुफ़्त।
2-min reads, plain English, every morning. Free forever.
