Every tool you use can leak your customers' information — here's how.
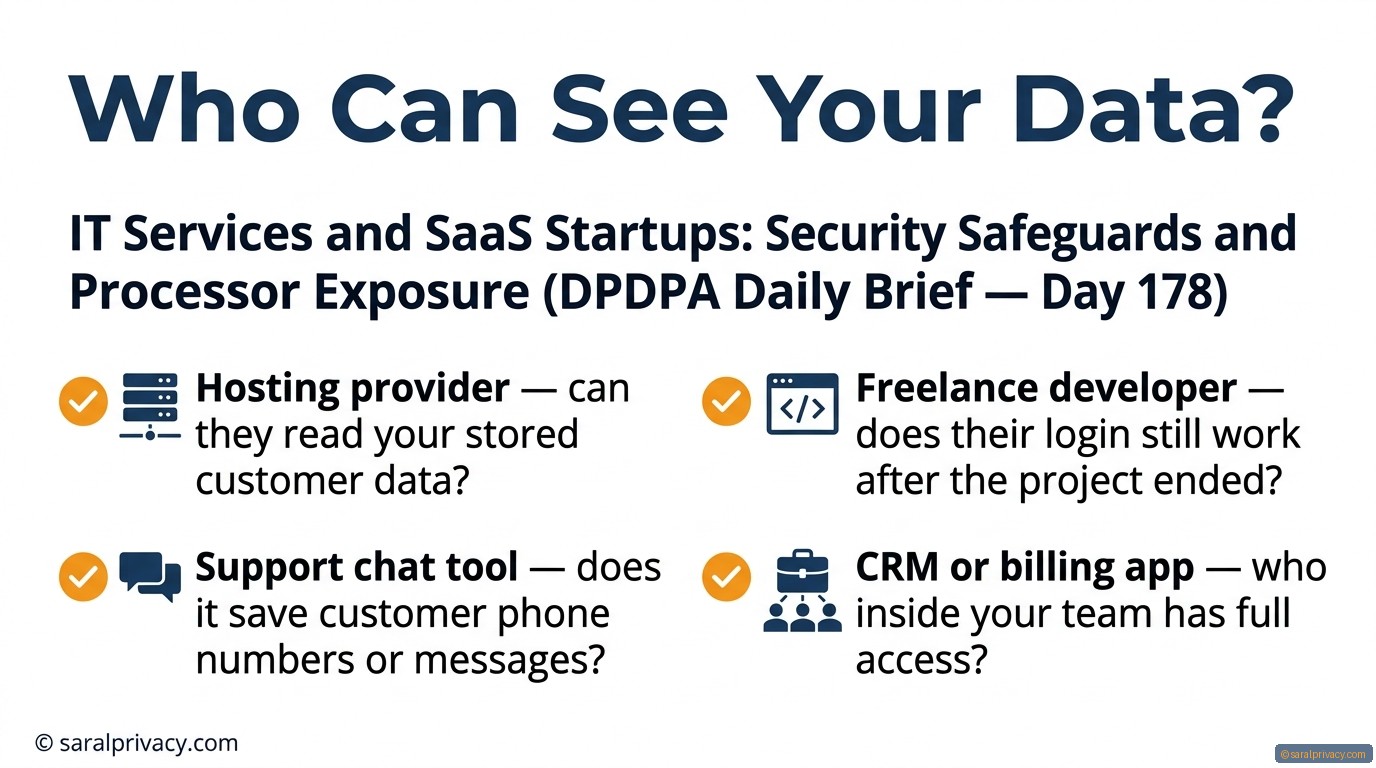
You use one app to store customer phone numbers. Another app for support. Another for billing. Each app can see your customers' information. Now imagine ten such apps. If even one is unsafe, your customers' data is at risk. Most IT startups and SaaS businesses do not count how many tools touch their data. That is a big mistake under India's new data law.
Say you run a small SaaS company. You store customer phone numbers and PAN card details. You use WhatsApp for support, a foreign CRM for leads, and a freelancer for coding. All three can see your customers' information. If any one of them leaks data, the law holds your business responsible. You must know who can see what. You must limit access. Only the right person should see the right information.
List every app and tool that touches your customers' information.
Remove access for any contractor or tool you no longer use.
Check if your business is ready. Takes 3 minutes. Visit saralprivacy.com/assessment
“Cloud scale does not excuse access sprawl.”
Free — takes 3 minutes
Answer a few simple questions. Get your free Readiness Score — sent to your email or WhatsApp.
Check My Readiness →Take our free 3–5 minute industry assessment to find out your compliance risk level.
Take Free Assessment →Free Download
The Complete DPDPA Compliance Guide
Plain English. Everything your business needs to understand the DPDP Rules 2025 — written for founders, not lawyers. Now in 7 Indian languages.
Download the Guide →5 Ready-to-Use Templates
Start complying — not just reading
Privacy Notice, Consent Language, Data Inventory, DSR SOP, Vendor Register. Delivered free to your email.
2-min reads, plain English, every morning. Free forever.
